Save Time
Use a tailored strategy to reduce risks instead of spending hours interpreting findings, investigating possible solutions or determining the best path to improve security.
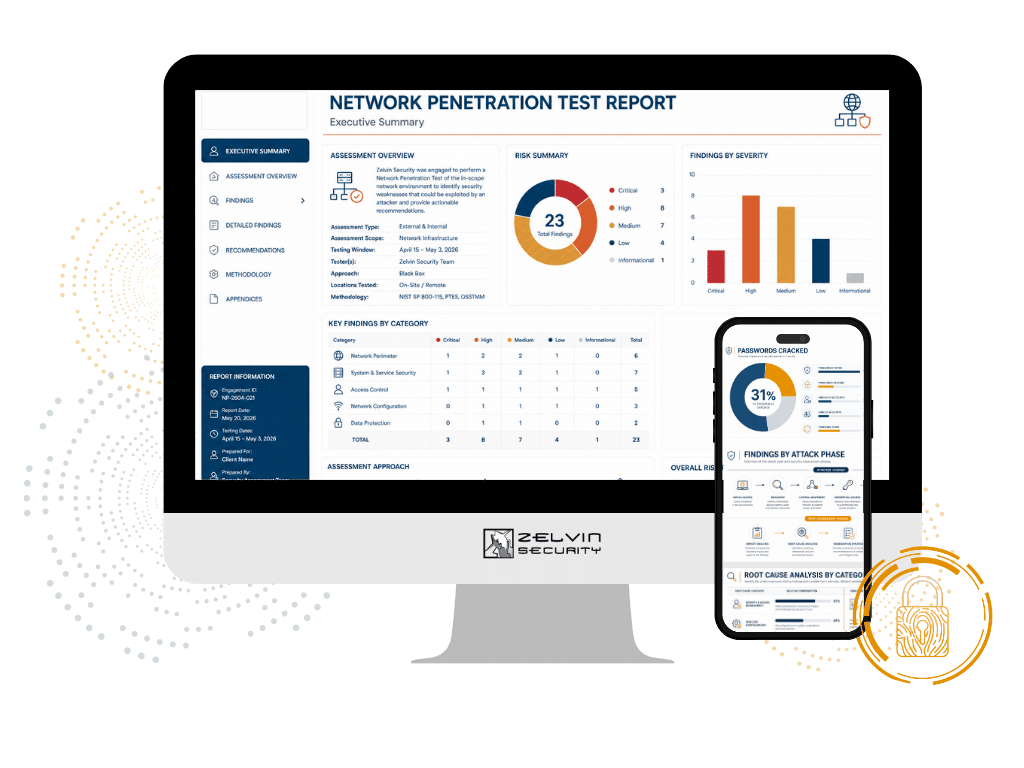
Identify exploitable network vulnerabilities, understand their business impact, and get a prioritized remediation plan from experienced penetration testers.
Understand how an attacker could move through your network and how to remediate existing risks.
Every network has a unique combination of systems, identities, permissions, security controls, and trust relationships. Zelvin's experienced penetration testers follow the evidence across those connections to uncover the attack paths that matter most to your organization.
We safely exploit and validate network vulnerabilities, investigate opportunities for lateral movement and privilege escalation, and determine whether an attacker could reach critical systems or sensitive data. We then connect that evidence to impact and root cause, giving your team a clearer understanding of where to focus, what to fix, and how to reduce risk efficiently.
The Final Report is more than evidence of exploitations. It is a tailored strategy for your network.
Work directly with experienced Ethical Hackers. The people performing your test help scope the engagement, understand your business, investigate the results, explain the impact, and remain available while your team works through remediation.
Success isn't measured by the number of vulnerabilities we find. Our goal is to help your team understand the risks, determine what matters most, and make informed security decisions based on evidence.
Get more value from the technology you already own with a custom remediation strategy. Before we hand over a report, our team considers your environment, root causes, existing tools, and security controls to develop practical recommendations.
Speak directly with Zelvin's testing team to design the test around your environment.
Vulnerability scanners, EDR, SIEM, firewalls, identity controls, and other security technologies provide important layers of protection. But knowing those controls exist isn't the same as knowing how they will perform during an attack.
Network penetration testing provides evidence-based results and outlines the path an attacker could take to compromise the infrastructure.
Our ethical hackers safely validate exploitable vulnerabilities to determine whether weaknesses can be combined, how far an attacker could move through the network, and how your defense tools respond.
Evaluate internet-facing systems and services from an attacker's perspective to uncover vulnerabilities, misconfigurations, and unintended exposure.
Testing proactively uncover weaknesses that could provide an attacker with an initial foothold in your organization.
Receive an analysis of look-alike domains that could be used to impersonate your organization, target employees or customers, or support social engineering attempts.
💰This service is included in your external penetration test at no additional cost.
Simulate real-world phishing, vishing, and smishing attacks to evaluate how users recognize and respond to social engineering. Identify human and process vulnerabilities, validate security awareness training, and uncover opportunities to improve security awareness.
Our penetration testers use techniques such as lateral movement, poisoning, and relay attacks to identify exploitable vulnerabilities and misconfigurations, determine how far an attacker could progress through your environment, and uncover attack paths that could put critical systems and data at risk.
The goal is to identify paths to sensitive data, elevated privileges, and critical network services.
Testing includes searching for Active Directory misconfigurations, excessive permissions, insecure authentication, credential exposure, and trust relationships that could create exploitable attack paths.
Our ethical hackers validate whether these weaknesses can be used to escalate privileges, move laterally, compromise privileged accounts, or gain access to sensitive systems and data.
Test segmentation controls and trust boundaries to determine whether an attacker can move between network segments, bypass access restrictions, and reach sensitive systems or data.
Zelvin's report provides a current view of VLAN rules and traversal, helping your team understand how network segments are connected today and make informed decisions about future system and service placement.
Securely crack user and service account password hashes to uncover weak, default, reused, and non-expiring passwords.
We also evaluate password policies against current security best practices to identify credential weaknesses that could lead to unauthorized access or elevated privileges.
Evaluate VPN configurations, authentication, access controls, and exposed services to identify vulnerabilities or weaknesses that could allow unauthorized remote access.
Zelvin's testing also validates what a compromised VPN user can access and whether network controls appropriately restrict movement beyond authorized resources.
Evaluate wireless networks, authentication, encryption, configurations, and access controls to uncover risks, vulnerabilities, and attack paths to other internal systems, sensitive resources, or other network segments.
After the internal penetration test, we'll relaunch selected attacks while your blue team observes, giving you the opportunity to validate the effectiveness of your alerting, monitoring, and detection tools. This helps demonstrate the value and effectiveness (ROI) of your existing defensive tools.
Purple teaming helps demonstrate the value of your defensive technology investments, identify gaps or delays in monitoring and alerting, and shorten detection and response times if an actual attack occurs.
Every network is different. Your architecture, users, systems, security controls, trust relationships, sensitive data, and business priorities should determine how your penetration test is designed.
That's why our assessment starts with understanding what you need the test to prove.
Scope & Proposal
We'll meet with your team to understand your environment, security concerns, objectives, compliance or contractual requirements, and the questions you need the penetration test to answer.
Our experienced testers help determine the appropriate scope, testing perspective, starting position, systems, attack scenarios, and methodology.
Then we'll provide a fixed proposal outlining the scope and testing strategy.
A well-executed network penetration test starts with asking the right security questions before testing starts.
Manual Testing by Humans Armed with AI
Our experienced ethical hackers remain responsible for your assessment while using AI, automation, proprietary technology, and hands-on techniques to increase efficiency and coverage.
Technology handles repeatable tasks efficiently, giving our testing team more time to investigate the areas that require human judgment.
AI gives our testers more time to:
🔒Investigate unusual results.
🔒Explore meaningful attack paths.
🔒Validate methodology coverage.
🔒Understand impact.
🔒Evaluate monitoring and detection.
🔒Identify root causes.
AI makes the time our pentesters spend more valuable.
Report, Retest, and Support
Report: Your report connects technical findings to evidence and impact, prioritizes the risks that matter, and provides a practical remediation strategy.
Whenever possible, recommendations consider security technology and controls you already own.
Retesting: Validate that remediation has resolved the identified weaknesses.
Support: Discuss identified risks with the Zelvin team for up to 12 months at no additional cost.
Attestation: Receive independent third-party evidence of testing for customers, compliance, regulators, and other stakeholders.
See how we turn findings into clear evidence, illustrate business impact, and outline practical guidance for every member of your team.
Zelvin stands out from the other companies because of the actionable operational advice they bring to the testing and to the report.
We've worked with other cybersecurity companies in the past, but with Zelvin, I am very satisfied with the results. They understood where we wanted to be.
Public Sector
Director of Technology
Zelvin understood our concerns and how the school operates. Their testing was thorough, their recommendations were realistic and they supported us all the way through to remediation.
K-12 School District
IT Director
This was our third project with Zelvin. They are great to work with. Their team understands what they are doing and sums it up in a way that makes sense. It is rare to find a partner who is technically strong and easy to work with.
Financial Services
Chief Information Security Officer
Experienced penetration testers provide the judgment to determine where to look deeper, how weaknesses connect, what an attacker could accomplish, and what your team should do next.
Before testing begins, an experienced penetration tester helps define the right external and internal attack surfaces, testing perspectives, network segments, critical systems, and objectives. The scope is built around your environment, and the security questions you need the assessment to answer.
A Zelvin penetration tester remains responsible for deeply testing the agreed methodology, attack scenarios, and testing objectives are covered.
This is a useful distinction because NIST describes penetration testing as going beyond automated vulnerability scanning and involving teams with demonstrable expertise, like Zelvin!
.
When the evidence leads somewhere, we follow it.
Network attacks rarely depend on a single vulnerability. Our testers investigate how exposed services, credentials, Active Directory weaknesses, misconfigurations, trust relationships, and segmentation gaps can be chained together to create an attack path, escalate privileges, or reach sensitive systems and data.
Did you know? Zelvin testers have the autonomy to spend up to 20% additional testing time following meaningful evidence when an assessment warrants deeper investigation, at no additional cost.
A vulnerability tells you what might be exploitable. Network penetration testing should tell you what happens next. Our testers validate whether a weakness can lead to credential compromise, lateral movement, privilege escalation, access to critical systems, or exposure of sensitive data so you can prioritize risk based on demonstrated impact.
Find out whether your defenses saw the attack.
We correlate network penetration testing activity with your monitoring and defensive tools to determine which attack techniques generated alerts, how quickly they were detected, and where visibility gaps exist.
Use the results to validate the value of your EDR, SIEM, IDS/IPS, logging, monitoring, and alerting investments and identify opportunities to improve detection.
Included with your Zelvin network penetration test at no additional cost.
Zelvin recommendations consider the attack path, root cause, network architecture, security controls, and technology already in your environment. When appropriate, we provide practical steps that help your team make better use of existing security investments before adding more technology.
Our team of penetration testers remain available to you as a subject matter expert when questions arise throughout your remediation stage. That's why we remain in close contact for up to 12 months after the engagement.
We stand behind our findings and are willing to support your team when they need it.
Retesting confirms whether remediation successfully closed the network attack path or vulnerability identified during testing. Retesting is outlined and defined in the SOW. Some organizations require retesting such as those seeking PCI DSS verification.
Plus, after the assessment, your Zelvin testing team remains available for up to 12 months to answer questions related to the findings.
Receive an independent attestation documenting completion of your network penetration test.
Use it to support customer security reviews, enterprise procurement, audits, compliance activities, cyber insurance requests, and other stakeholders that need evidence of independent security testing.
Our methodology satisfies regulations and meets standards such has NIST, HIPAA, security rule compliance including the December 2025 proposed cybersecurity rule.

K–12 & Education
Identify practical ways to reduce network risk across complex environments with diverse users, devices, systems, and limited resources.
Public Sector
Independently validate network controls, segmentation, access, and potential attack paths across critical systems.
Professional Services
Protect client information and business-critical systems by identifying vulnerabilities, access weaknesses, and paths through the network.
SaaS & Technology
Validate network infrastructure, identities, access controls, and attack paths that could expose applications, systems, or customer data.
Financial Services
Identify attack paths, segmentation weaknesses, and access risks across highly regulated financial environments.
Healthcare
Evaluate vulnerabilities and attack paths that could lead to sensitive systems, connected infrastructure, or protected data.
To highlight our commitment to the craft of Ethical Hacking and to illustrate our high ethical standards, we became a CREST Pathway+ member.
Ethical Hacking is both an art and a science. Our team is focused on consistent, trusted results through methodologies designed using decades of experience, new AI tools, and industry-recognized standards.
Offensive Security Certified
Professional (OSCP)
GIAC Web Application
Penetration Tester
(GWAPT)
GIAC Certified
Incident Handler
(GCIH)
GIAC Security Essentials
(GSEC)
Get answers, get a testing plan, and design the best approach to meet your goals.
Proactively understand how an attacker could gain access, escalate privileges, and reach sensitive systems or data to disrupt business operations.
Identify exploitable vulnerabilities, misconfigurations, excessive permissions, and attack paths across your interconnected cloud environment to reduce security risks, proactively.
Validate the security of web applications, APIs, mobile applications, and AI-enabled technologies with trusted third-party results to support customers, compliance, and due diligence requirements.
Our approach is designed to reduce the time, cost, and uncertainty that can follow security testing while helping your team turn identified risks into meaningful improvements.
Use a tailored strategy to reduce risks instead of spending hours interpreting findings, investigating possible solutions or determining the best path to improve security.
Use the tools and security investments you've already made and are familiar with to strengthen your security.
Zelvin's team is accessible to provide guidance and technical expertise for up to 12 months after the penetration test report is delivered.
Use independent, third-party evidence to support customers, auditors, regulators, and executive leadership.