Save Time
Use a tailored strategy to reduce risks instead of spending hours interpreting findings, investigating possible solutions or determining the best path to improve security.
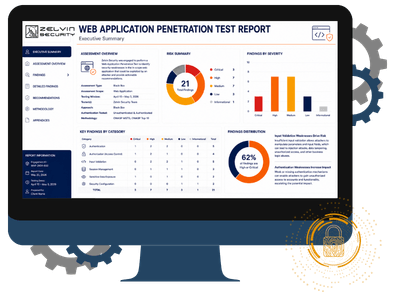
Zelvin Security provides independent, human-led penetration testing for web applications, SaaS platforms, APIs, mobile applications, and AI-enabled applications.
Modern applications depend on interconnected functionality, APIs, cloud services, third-party integrations, user roles, identities, and sensitive data. Zelvin’s penetration testers safely identify and validate exploitable vulnerabilities, then investigate how individual weaknesses could be combined to create broader attack paths.
Our testing evaluates whether an attacker could bypass authentication or authorization controls, cross user or tenant boundaries, escalate privileges, manipulate application workflows, abuse APIs or integrations, access restricted functionality, or expose sensitive data.
Human-led testing provides context that automated findings alone cannot. A vulnerability that appears limited can become significantly riskier when combined with input validation problems, excessive permissions, authorization gaps, exposed APIs, insecure workflows, compromised accounts, or other weaknesses.
You'll receive results that will stand up to compliance and strict due diligence programs and guidance to remediate risk without slowing down innovation.
The scope is tailored to your organization to keep pricing lean and meet your objectives. Request a confidential, no obligation proposed scope from our Ethical Hacking team.
Zelvin’s penetration testers use decades of experience to evaluate web applications from an attacker’s perspective, identifying the risks that matter and helping your team address them. This expertise delivers better value to your organization.
Independent. Objective. Expert-Led.
Independent third-party testing provides results, technical judgement, and decades of offensive security testing expertise.
Actionable Reporting
The Zelvin Report prioritizes risk and provides clear remediation guidance, helping your team fix issues faster.
Retesting Included
Retesting is built into every engagement to validate fixes and keep remediation moving.
Letter of Attestation
Zelvin provides independent evidence of third-party security testing for customers, procurement teams, security reviews, and governance programs.
Receive evidence that your application has undergone independent security testing that exceeds customer and governance program requirements.
We evaluate the controls that determine who can access your application and what authenticated users are permitted to do.
Testing may include authentication mechanisms, session management, password and account recovery workflows, multi-factor authentication implementations, horizontal and vertical privilege escalation, object-level authorization, administrative functions, and role-based access controls.
For multi-user and SaaS applications, testing can also evaluate whether users can cross account, organization, or tenant boundaries to access data or functionality they should not be able to reach.
Some of the most consequential application vulnerabilities are specific to how an application is designed to work.
Our penetration testers analyze workflows, roles, transactions, state changes, and business rules to identify opportunities to manipulate intended processes, bypass restrictions, perform actions out of sequence, or abuse legitimate functionality in unintended ways.
These risks often require human reasoning and application context to identify because the individual requests may appear technically valid to automated tools.
We evaluate whether users can access data, functionality, administrative capabilities, or resources beyond their intended permissions. Testing includes privilege escalation, object-level authorization, forced browsing, role manipulation, and tenant-boundary violations, to name a few.
Testing evaluates how the application handles untrusted input and whether data can be manipulated in ways that affect application behavior, security controls, or downstream systems. This can include injection vulnerabilities, file handling, parameter manipulation, server-side processing, and other application-specific input risks.
We evaluate whether security-relevant application activity generates appropriate logs and alerts and whether application responses or errors expose information useful to an attacker.
For applications incorporating AI agents, assistants, LLMs, or agentic workflows, testing evaluates whether AI functionality can be manipulated to access data, invoke tools or APIs, cross authorization boundaries, disclose sensitive information, or perform unintended actions.
Testing may include direct and indirect prompt injection, excessive agency, tool and API abuse, authorization enforcement, sensitive-data exposure, agent workflows, memory and context manipulation, and trust relationships between AI components
Work directly with experienced Ethical Hackers. The people performing your test help scope the engagement, understand your business, investigate the results, explain the impact, and remain available while your team works through remediation.
Success isn't measured by the number of vulnerabilities we find. Our goal is to help your team understand the risks, determine what matters most, and make informed security decisions based on evidence.
Get more value from the technology you already own with a custom remediation strategy. Before we hand over a report, our team considers your environment, root causes, existing tools, and security controls to develop practical recommendations.
Speak directly with Zelvin's testing team to design the test around your environment.
Our team's experience helps shape the engagement before testing begins, providing important insight into the right scope, testing perspectives, and objectives. This includes testing perspectives, roles, functionality, APIs, integrations, and other unique factors related to your application environment.
A Zelvin penetration tester is responsible for ensuring the agreed methodology, scope, and testing objectives are thoroughly addressed. Methodologies are informed by industry resources, including applicable OWASP resources, and OWASP Top 10 while giving our testers the flexibility to investigate risks that standardized checklists and automated tools may not identify.
When something unexpected appears or weaknesses can be chained together, our team investigates further to understand the risks, validate the impact, and provide evidence-based recommendations.
When evidence warrants further investigation, our testers have the flexibility to follow it. Testing is driven by what we learn during the engagement, not simply by completing a predefined checklist.
💡DID YOU KNOW?
Our testers have the autonomy to spend up to 20% additional time following evidence when an assessment warrants deeper investigation, at no additional cost.
We prioritize quality over quantity every time.
Our experienced team understands how an application is intended to work and investigates how legitimate functionality could be manipulated in ways an automated scanner may not recognize.
We cross-reference testing activity with your defensive tools to help determine which exploits generated alerts, how quickly they were identified, and where visibility gaps may exist.
💰Validate the effectiveness of your monitoring, alerting, and detection investments.
This validation is included with your penetration test at no additional cost.
Your developers and security professionals can discuss findings with the people who performed the testing. That helps teams understand root cause, potential impact, and remediation—not simply read a vulnerability description.
Our team of penetration testers remain available to you as a subject matter expert when questions arise throughout your remediation stage. That's why we remain in close contact for up to 12 months after the engagement.
We stand behind our findings and are willing to support your team when they need it.
We know you're not simply looking for a report. Your goal is to use objective, third-party results to accelerate business deals, compliance requirements, or stakeholder confidence that your applications security controls have been independently evaluated.
That's why retesting is so important. Retesting hours are included in web application penetration testing, and we'll promptly perform retesting when your team is ready.
Our penetration testers also remain available for up to 12 months after the engagement to answer questions about findings and support your team through remediation.
If your organization is required by regulatory compliance or has contractually committed to following security standards, confirm that the testing methodology satisfies the requirements.
Some requirements establish expectations around tester qualifications, independence, methodology, remediation, retesting, or third-party assurance.
Zelvin puts experienced penetration testers in control of the engagement and uses AI and automation to increase their efficiency, not replace them.
AI-assisted techniques help our testers accelerate research and analysis, organize evidence, investigate complex functionality, and spend more engagement time pursuing meaningful attack paths.
The human penetration tester remains responsible for testing decisions, validation, risk interpretation, and the findings delivered to your team.
Zelvin stands out from the other companies because of the actionable operational advice they bring to the testing and to the report.
We've worked with other cybersecurity companies in the past, but with Zelvin, I am very satisfied with the results. They understood where we wanted to be.
Public Sector
Director of Technology
Zelvin understood our concerns and how the school operates. Their testing was thorough, their recommendations were realistic and they supported us all the way through to remediation.
K-12 School District
IT Director
This was our third project with Zelvin. They are great to work with. Their team understands what they are doing and sums it up in a way that makes sense. It is rare to find a partner who is technically strong and easy to work with.
Financial Services
Chief Information Security Officer
To highlight our commitment to the craft of Ethical Hacking and to illustrate our high ethical standards, we became a CREST Pathway+ member.
Ethical Hacking is both an art and a science. Our team is focused on consistent, trusted results through methodologies designed using decades of experience, new AI tools, and industry-recognized standards.
Proactively understand how an attacker could gain access, escalate privileges, and reach sensitive systems or data to disrupt business operations.
Identify exploitable vulnerabilities, misconfigurations, excessive permissions, and attack paths across your interconnected cloud environment to reduce security risks, proactively.
Passwords are essential to security. Find out more about Password Security best practices and the entropy of your current password.
Get Password Cracking As A Service with your next penetration test.
Our approach is designed to reduce the time, cost, and uncertainty that can follow security testing while helping your team turn identified risks into meaningful improvements.
Use a tailored strategy to reduce risks instead of spending hours interpreting findings, investigating possible solutions or determining the best path to improve security.
Use the tools and security investments you've already made and are familiar with to strengthen your security.
Zelvin's team is accessible to provide guidance and technical expertise for up to 12 months after the penetration test report is delivered.
Use independent, third-party evidence to support customers, auditors, regulators, and executive leadership.